
AI is now part of everyday business. Companies use AI to write content, create code, study data, answer customer questions, search information, and help with decisions.
New AI agents can do even more. They can connect with business tools, use data, and take actions.
This creates an important question. Who controls the AI, and who is responsible if something goes wrong?
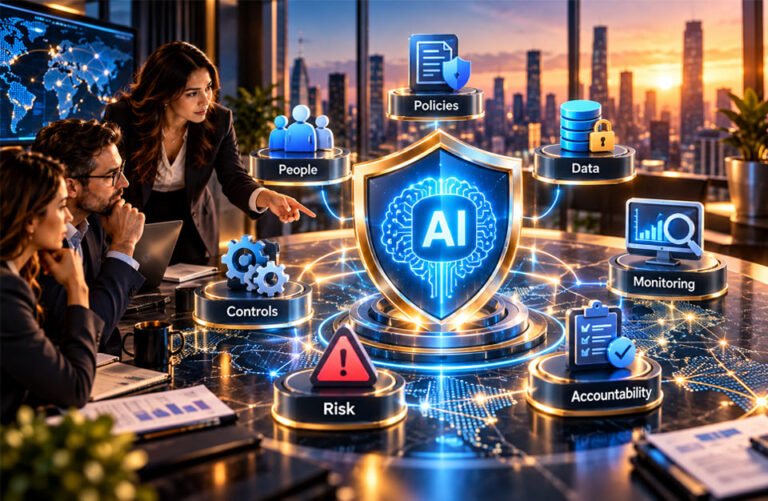
This is why AI transformation is a problem of governance. Companies need clear rules for ownership, risk, data, permissions, human review, monitoring, and responsibility.
This guide explains how companies can use AI safely while keeping people in control.
What Does “AI Transformation Is a Problem of Governance” Mean?
AI transformation is a problem of governance means that using AI successfully is not only about having good technology.
A company may have a powerful AI model. But it still needs to decide how that AI should be used.
For example, the company must decide what data the AI can see, what tasks it can perform, and how much control it should have.
AI governance is the set of rules, processes, responsibilities, and controls used to manage AI. It covers the full life of an AI system, from approval and development to monitoring and retirement.
Technical teams may build and connect the AI. Business teams may decide how they want to use it. Governance makes it clear who has authority and who is responsible.
Companies should answer some basic questions:
- Who can approve the AI system?
- Who is responsible for its results?
- What information can it use?
- What decisions can it make or influence?
- When does a person need to check its work?
- Who can stop the AI?
- What happens if it makes a serious mistake?
AI can make a recommendation or take an action. However, the company is still responsible for how the system is used.
Companies therefore need to govern more than the AI model. They must also think about its data, users, permissions, connected systems, decisions, and possible risks.
The main question is not only “What can AI do?” It is also “What should AI be allowed to do, and who is responsible for it?”
Why Traditional IT Governance Is Not Enough
Normal IT governance is still important. Companies need cybersecurity, access controls, system management, and clear rules for making changes.
However, AI creates some different problems.
Traditional software normally follows programmed rules. AI models can be less predictable.
Generative AI creates answers based on patterns and context. Its answer can change depending on the prompt, data, model version, and other information it receives.
AI can also give an answer that sounds correct but is actually wrong. This is often called an AI hallucination.
AI risks can also change after a system is launched.
The model may be updated. Employees may start using it in new ways. The AI may get access to new data or tools. Security threats and legal requirements can also change.
This means companies should not approve an AI system once and then forget about it.
AI governance should continue through the full AI lifecycle. This includes planning, development, testing, launch, normal use, monitoring, updates, and retirement.
The NIST AI Risk Management Framework (AI RMF) uses four main functions:
Govern means setting rules, responsibilities, and accountability.
Map means understanding the AI system, its purpose, users, and risks.
Measure means testing the system and measuring its risks and performance.
Manage means deciding how risks should be controlled.
Governance should therefore continue throughout the life of an AI system.
AI Governance Starts With the Use Case
Companies should not judge AI risk only by looking at the model.
The same AI model can be used for very different jobs.
For example, an employee may use AI to fix grammar in an internal presentation. The risk is usually low.
A customer service team may use the same AI to answer customers directly. A wrong answer could now affect customers.
A financial company may use the same technology to help review suspicious transactions. A mistake in this situation could have much bigger effects.
The AI model may be similar, but the level of risk is different.
Companies therefore need to understand how the AI will actually be used.
They should know who will use it, what data it can see, what decisions it can affect, and what systems it can access.
They should also know whether a person checks the AI’s work and what could happen if the system makes a mistake.
Good AI governance looks at the complete use case, not only the model.
Ownership and Decision Rights
Every important AI system should have a clear owner.
This can be difficult because many teams may be involved.
IT may manage the technology. A third-party company may provide the AI model. A business team may choose how to use it. Security may control access. Legal and compliance teams may set rules.
When many teams are involved, it can become unclear who is responsible.
A company should therefore name a person, team, or business function that owns each important AI system.
The owner does not need to do every technical task. However, the owner should understand why the system is being used, its main risks, and the controls around it.
The owner should also know whether the AI is still safe and useful enough to remain active.
Decision Rights
Decision rights explain who has the power to make important choices about an AI system.
For example, a company should know who can approve the system, change its permissions, accept a risk, pause it, or shut it down.
This becomes especially important when AI affects hiring, finance, insurance, pricing, safety, or other important areas.
If responsibility is not clear, different teams may assume someone else is responsible.
Companies cannot simply say “the AI did it” when something goes wrong.
Someone still approved the AI, gave it access, and decided how it could be used.
Risk Classification and Proportional Controls
Not every AI system needs the same level of control.
A simple AI writing tool normally creates less risk than an AI system involved in hiring, healthcare, lending, insurance, or financial decisions.
Companies can therefore place AI systems into different risk levels.
Several things can help decide the risk:
- Authority: What decisions can the AI make?
- Autonomy: What can it do without asking a person?
- Scale: How many people or transactions can it affect?
- Sensitivity: Does it use private or sensitive information?
- Possible harm: What could happen if it makes a mistake?
- Reversibility: Can the mistake easily be fixed?
Higher-risk systems should normally have stronger controls.
Companies should also think about the decision the AI is making, not only the model behind it.
For example, AI recommending a restaurant is very different from AI recommending medical treatment.
An AI system organizing documents is also very different from one helping decide whether a person receives a loan.
The greater the possible harm, authority, scale, and autonomy, the stronger the governance should be.
AI Agents Create New Governance Risks
Normal AI assistants mainly give answers or create content.
AI agents can also take actions.
For example, an AI assistant may tell an employee that a customer should receive a refund.
An AI agent may be able to issue the refund itself.
An agent could also read information from a customer database, write an email, send it, update the customer record, and start another task.
AI agents may combine several abilities.
Reasoning helps the agent decide what to do next.
Memory helps it use information from earlier tasks or conversations.
Tools allow it to connect with databases, email, APIs, browsers, and business software.
Autonomy allows it to complete tasks without asking a person at every step.
These abilities can make AI agents useful. They can also increase risk.
Companies need clear rules about what an agent can and cannot do.
Can it spend money? Can it delete information? Can it contact customers? Can it create accounts? Can it approve transactions? Can it change important software?
Companies also need to decide when a person must approve an action.
This is why permissions are very important for AI agents.
A powerful AI with limited access may create less risk than a less powerful AI that has full access to sensitive systems.
Guardrails, Permissions, and Access Controls
AI guardrails are technical limits placed around an AI system.
They can block harmful content, protect sensitive information, limit access to tools, stop certain actions, or require human approval.
Guardrails are useful, but they are not the same as AI governance.
A guardrail tells the AI what it cannot do.
Governance decides why that rule exists, who approved it, who checks it, and what happens if it fails.
For example, a company may allow an AI buying agent to make purchases below a certain amount.
The system can enforce that limit. But the company still needs to decide why that amount is safe and who approved it.
The company should also watch for unusual behavior. An AI agent might make many small purchases that stay below the limit but still create a large total cost.
Limit Access and Authority
Companies should give AI only the access it needs.
For example, an AI agent that only needs to read customer records should not automatically be allowed to change or delete them.
The same rule applies to email, financial systems, company data, code, and other important tools.
Companies should also decide when human approval is required and who has the power to stop the AI.
Good governance combines permissions, guardrails, monitoring, testing, clear rules, and human responsibility.
Data Governance, Privacy, and Security
AI systems often need data to work well.
Companies should know where their data comes from, who owns it, and who is allowed to use it.
They should also know whether the data is suitable for AI.
Employees need clear rules about what information they can enter into AI tools.
Customer details, contracts, source code, financial records, personal information, and private company documents may need extra protection.
Companies should also understand what an outside AI provider does with submitted information.
For example, does the provider store prompts? How long is the information kept? Can it be used to train AI models?
AI agents create another concern. A worker may have permission to view certain information, but an AI agent may not need the same level of access.
Agents may also combine information from different databases. This can create new privacy and security risks.
Good data governance should cover access, privacy, security, data storage, intellectual property, contracts, and proper AI use.
Shadow AI and Unapproved Tools
Shadow AI happens when workers use AI tools that their company has not approved.
Employees may use these tools because they make work faster or easier.
The risk begins when workers enter private company information into an unapproved AI service.
This may include customer details, contracts, source code, financial information, business plans, or internal documents.
The company may not know where this information is stored or how the AI provider uses it.
Simply banning outside AI tools may not always work.
Companies should provide useful approved tools and clear rules about what workers can and cannot do.
Employees should also receive simple training about sensitive information.
Access controls and logging can provide extra protection.
Companies should also make it easy for workers to request approval for a new AI tool.
Shadow AI can sometimes show that workers need a type of AI tool that the company does not currently provide.
Human Oversight Must Have Real Authority
Human oversight can help reduce AI risk.
However, simply adding a person to the process is not enough.
The reviewer needs enough information, time, knowledge, and authority to question the AI.
Scale can make this difficult.
A person may carefully review 20 AI recommendations. Reviewing 20,000 recommendations in the same way may be impossible.
People may then start accepting AI results without checking them properly. This is sometimes called automation bias.
There are different forms of human oversight.
Human in the loop means a person approves individual actions.
Human on the loop means AI works automatically, while a person watches it and can step in.
Human over the loop means people create the rules and limits under which the AI works.
The right type depends on the level of risk.
Most importantly, the person responsible for oversight should be able to reject, change, pause, or escalate an AI decision.
Logging, Traceability, and Explainability
Companies should be able to understand what happened when an AI system makes an important decision.
For example, imagine an AI agent rejects a customer’s request.
The company may need to know what information the AI received, which model was used, what instructions it followed, which tools it used, and whether a person reviewed the decision.
This requires good records.
An AI decision chain may look like this:
User → Agent → Model → Tool → Database or External Service → AI Decision → Human Approval → Final Action
Companies do not need to record everything in exactly the same way. The level of logging should match the system and its risks.
Version records can also help. A company should know which model, instructions, policies, and settings were being used when an important event happened.
These records can help with investigations, customer complaints, audits, security problems, and legal requirements.
Explainability is also important.
People should have enough information to understand and review important AI-supported decisions.
Continuous Monitoring After Deployment
AI governance does not stop when a system is launched.
AI systems can change over time.
Data may change. Models may be updated. Workers may use the AI differently. Vendors may add new features.
AI agents may also receive new tools or permissions.
Companies should therefore continue watching important AI systems.
They may monitor output quality, errors, security problems, unusual behavior, data changes, model drift, and whether the system is staying within its approved limits.
The level of monitoring should depend on risk.
A simple internal writing assistant does not need the same monitoring as an AI system making thousands of important customer decisions.
Companies should also set clear limits.
If the AI moves outside those limits, someone should know when to investigate, restrict, or stop it.
AI Incident Management
Companies should prepare for AI problems before they happen.
An AI incident may involve a harmful answer, serious error, data leak, security failure, or action that the AI was not allowed to perform.
A company should know who receives the alert and who investigates the problem.
It should also be clear who has the power to pause or shut down the AI system.
Important logs and records should be saved for the investigation.
The company should look for the real cause of the problem. The issue could come from the model, data, prompt, permissions, integration, or human review process.
If customers or other people were affected, the company may need to correct the result.
Some incidents may also need to be reported under applicable laws or regulations.
After an incident, the company should review its controls and reduce the chance of the same problem happening again.
Third-Party AI and Vendor Governance
Many businesses use AI from outside providers.
Using a trusted AI provider does not mean the provider is responsible for everything.
Different companies may control different parts of the system.
One company may provide the AI model. Another may provide cloud services. Another may provide the software.
The business using the AI still decides how it is used, what data it can access, and which decisions it can affect.
Companies should therefore review AI vendors carefully.
They should check areas such as privacy, security, data storage, legal requirements, model limits, and important service changes.
Vendor checks should continue after the company starts using the service.
AI providers can change their models, features, terms, and data practices.
Companies should understand which risks are controlled by the vendor and which risks remain their own responsibility.
AI Laws, Standards, and Governance Frameworks
AI governance is becoming more closely connected with laws and formal standards.
Rules can be different from one country to another.
The EU AI Act uses a risk-based system. Different rules apply depending on the type of AI and how it is used.
Some transparency requirements became applicable on August 2, 2026. These include rules for certain AI interactions and some AI-generated or changed content.
Other parts of the EU AI Act follow different dates and requirements.
Companies should therefore check which rules apply to their specific AI systems.
The NIST AI Risk Management Framework is another important framework. It uses four main functions: Govern, Map, Measure, and Manage.
ISO/IEC 42001 provides requirements for an AI management system. It helps organizations create, maintain, and improve their approach to AI management.
The OECD AI Principles cover areas such as accountability, transparency, safety, human-centered values, and AI risk management.
These laws and frameworks are not all the same.
For example, the NIST AI RMF is a voluntary framework. A binding law can create legal duties.
Companies working in different countries may therefore need to follow several rules at the same time.
How to Build an AI Governance Framework
A company can start by deciding where it wants to use AI and what level of risk it is willing to accept.
Next, it should create an AI inventory.
This is a record of important AI systems being used in the company. It may include AI models, agents, outside AI services, and AI features inside other software.
Each important AI system should have a clear owner.
The company should then decide the risk level of each use case.
Higher-risk systems should receive stronger checks and controls.
Companies should also map what data and systems the AI can access.
Permissions and decision rights should be clear. The company should know what AI can do alone and what needs human approval.
Important AI systems should be tested before launch.
Useful documentation may include the system’s purpose, owner, data sources, known limits, permissions, test results, and monitoring needs.
Companies should also create rules for monitoring and AI incidents.
Third-party AI services should be included in the same governance process.
Governance should continue when the system changes.
A major change to the model, data, vendor, permissions, or integrations may require another risk review.
How to Measure AI Governance
Companies should check whether their AI governance is actually working.
A good starting point is knowing how many important AI systems are being used.
The company can check whether each important system has an owner and whether required testing, risk reviews, documentation, and monitoring have been completed.
It can also track AI incidents, model drift, governance exceptions, and missed human reviews.
Another useful measure is how quickly the company finds and fixes AI problems.
Different systems need different measurements.
A customer support AI may be measured by answer quality and escalation rates.
A financial AI system may need very different measures.
The goal is not to create one perfect governance score.
The goal is to find problems early and give managers enough information to make better decisions.
The Role of Boards and Executives
AI governance should not be left only to technical teams.
Senior leaders do not need to understand every technical detail of an AI model.
However, they should understand the important business questions.
Capability: What can the AI do?
Autonomy: What can it do without human approval?
Access: What information and systems can it use?
Authority: What decisions can it make?
Scale: How many people or transactions can it affect?
Reversibility: Can a mistake be fixed?
Traceability: Can the company understand what happened?
Ownership: Who is responsible?
Control: What stops the AI from doing something unacceptable?
Escalation: What happens when there is a problem?
Senior leaders can also decide how much AI risk the company is willing to accept.
High-risk systems may need approval from senior management or a special AI governance group.
AI can automate work, but it does not remove management responsibility.
How Good Governance Can Speed Up AI Adoption
AI governance does not always have to slow down innovation.
Clear rules can actually help companies use AI faster.
Without a common system, every new AI project may need separate discussions about security, data, ownership, testing, legal issues, and monitoring.
A standard governance process makes these requirements easier to understand.
Low-risk projects can use a simpler approval process.
Higher-risk systems can receive stronger checks.
Companies can also build governance controls into AI systems from the beginning. This is sometimes called governance by design.
For example, access controls, logging, human approval, and monitoring can be added while the system is being built.
Documentation can also be created during development instead of waiting until the end.
Good governance creates a clear path for moving AI from testing into real business use.
A Practical AI Governance Checklist
Before using an important AI system, a company should ask:
- Do we know which AI systems are being used?
- Does each system have a clear purpose?
- Is there a clear owner?
- Has the risk level been checked?
- Do we know what data the AI uses?
- Does the AI have only the access it needs?
- Do we know what actions an AI agent can take?
- Are important actions recorded?
- Is human review available when needed?
- Has the system been tested?
- Is the system monitored after launch?
- Are major changes reviewed?
- Can someone quickly stop the AI?
- Is there a plan for AI incidents?
- Have relevant laws and company rules been checked?
- Is there a process for updating or retiring the system?
Not every AI tool needs the same controls.
The level of control should match the level of risk.
Bottom Line
AI transformation is a problem of governance because AI can change how companies use information, make decisions, and complete work.
Technology decides what AI can do. Governance decides what AI should be allowed to do.
Companies need clear ownership, safe permissions, good data controls, human oversight, monitoring, and clear responsibility.
These controls become even more important as AI agents gain more access and independence.
Good governance is not about stopping companies from using AI. It is about helping them use AI safely while keeping people responsible for important decisions.
Frequently Asked Questions
Why is AI transformation a problem of governance?
AI can use data, make decisions, and take actions. Companies need rules to control AI and decide who is responsible.
What is AI governance?
AI governance means the rules used to manage AI safely. It covers data, risks, access, human review, security, and responsibility.
How is AI governance different from IT governance?
IT governance manages normal technology and systems. AI governance also handles AI risks, changing results, data use, and human control.
Why do AI agents need stronger governance?
AI agents can use tools and take actions on their own. Companies need clear limits, permissions, and monitoring to control them.
Are AI guardrails the same as AI governance?
No. Guardrails are limits that control what AI can do. AI governance is the wider system of rules, controls, and responsibilities.
What is Shadow AI?
Shadow AI is when workers use AI tools that their company has not approved. It can create privacy, data, and security risks.
Who is responsible when AI makes a mistake?
The company and responsible people remain accountable for how AI is used. Responsibility should not simply be placed on the AI.
How can a company start AI governance?
Start by finding the AI tools being used and giving them clear owners. Then check risks, control access, monitor them, and set rules for problems.
Discover More:
ERACTOLL Complete Guide: Charges, Fees, Receipts, and Disputes
